Standard
ISO 9001:2026
Quality management for processes, responsibilities, indicators, customers and continual improvement.
Learn more →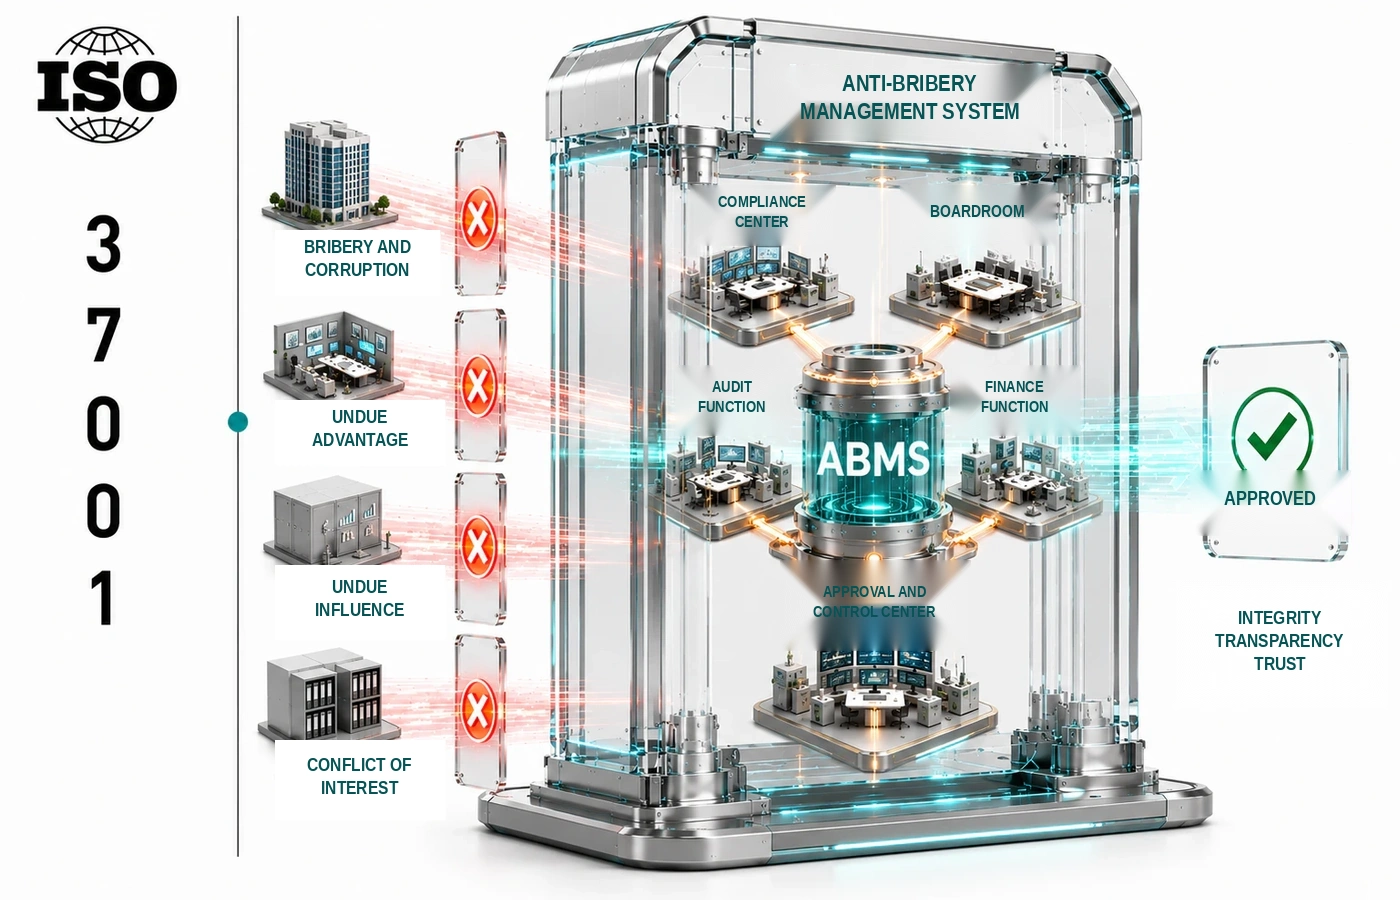
ISO 37001:2025 implementation, anti-bribery system, preventing, detecting and addressing bribery, due diligence, third parties, anti-bribery function, internal audit and certification preparation.
ISO 37001:2025 is the international standard for anti-bribery management systems. It provides requirements and guidance for preventing, detecting and addressing bribery, covering direct and indirect risks, third parties, internal functions, due diligence, financial and non-financial controls, reporting and corrective actions.
Official title of the standard: ISO 37001:2025 — Anti-bribery management systems — Requirements with guidance for use.
QMS Consulting provides ISO 37001:2025 consulting for organizations that want a clear, applicable and auditable system. The aim is not just to obtain the certificate, but to build a system that supports process control, compliance and continual improvement.
ISO 37001:2025 is the updated edition of the anti-bribery standard and includes clarifications on compliance culture, conflicts of interest, the anti-bribery function and alignment with modern compliance practices. Organizations that worked with the previous edition must analyze the new requirements and the transition.
ISO 37001:2025 requires anti-bribery controls proportionate to the organization's bribery risk. A company that deals with authorities, intermediaries or large projects needs a different level of control than one with simple commercial relationships.
The bribery risk assessment is the foundation of the system. Due diligence, financial controls and rules for gifts or sponsorships must follow from this assessment, not be copied from a generic model.
ISO 37001:2025 implementation starts from the real bribery risks and the commitment of top management. Each stage produces controls and evidence that can be verified by the compliance function and at the audit.
We compare existing integrity and compliance policies and controls with the requirements of the 2025 edition of the standard.
We analyze activities, markets, partners and interactions with authorities to assess where bribery risk arises.
We define the anti-bribery policy, the roles of top management and the anti-bribery compliance function, with the necessary independence and authority.
We set the level of checks for partners, intermediaries, suppliers and projects, proportionate to the risk identified.
We define financial and non-financial controls for payments, gifts, hospitality, sponsorships, donations and conflicts of interest.
We set up confidential reporting channels, protection for people who report concerns and how concerns are investigated.
We carry out the internal audit, support the management review and prepare the organization for the certification audit.
ISO 37001 certification is obtained through an audit carried out by an independent certification body chosen by the organization. Consulting does not replace the audit: it prepares the system and the team for it.
The organization selects a certification body with valid accreditation for this standard, where accreditation exists, and agrees the audit dates with it.
The body reviews the documentation, the scope of the system and the organization’s readiness for stage 2. Points to fix before continuing may be raised.
The body verifies on site that the system is implemented and effective, through interviews, observation and evidence. Nonconformities found are closed through corrective actions.
After nonconformities are closed, the body takes the certification decision and issues the certificate. The system is then checked through surveillance and recertification audits, according to the body’s rules.
At every stage, a consultant dedicated to the project and consultants experienced in certification audits prepare the evidence, the team and the responses to nonconformities. The certificate is issued only by the certification body. See ISO certification preparation.
Risks are assessed by activity, partner and market, and controls are applied where the risk is real.
Partners, intermediaries and sensitive transactions go through due diligence proportionate to the risk.
The organization can demonstrate a working anti-bribery programme to customers, investors and authorities.
Checks, approvals and decisions are documented and can be presented in partners' compliance audits.
Employees know the rules on gifts, conflicts of interest and reporting, and feel confident raising concerns.
Reporting channels and the investigation procedure allow concerns to be addressed before they become major incidents.
ISO 37001:2025 is relevant for organizations that work with public institutions, take part in tenders, use intermediaries or operate in sectors with a high risk of corruption, such as construction, energy, healthcare and infrastructure.
ISO 37001:2025 integrates with ISO 9001 and other compliance systems, so that anti-bribery controls use the same internal audit, corrective action and management review processes.
Quality management for processes, responsibilities, indicators, customers and continual improvement.
Learn more →
Information security for information risks, the ISMS, controls, access and data.
Learn more →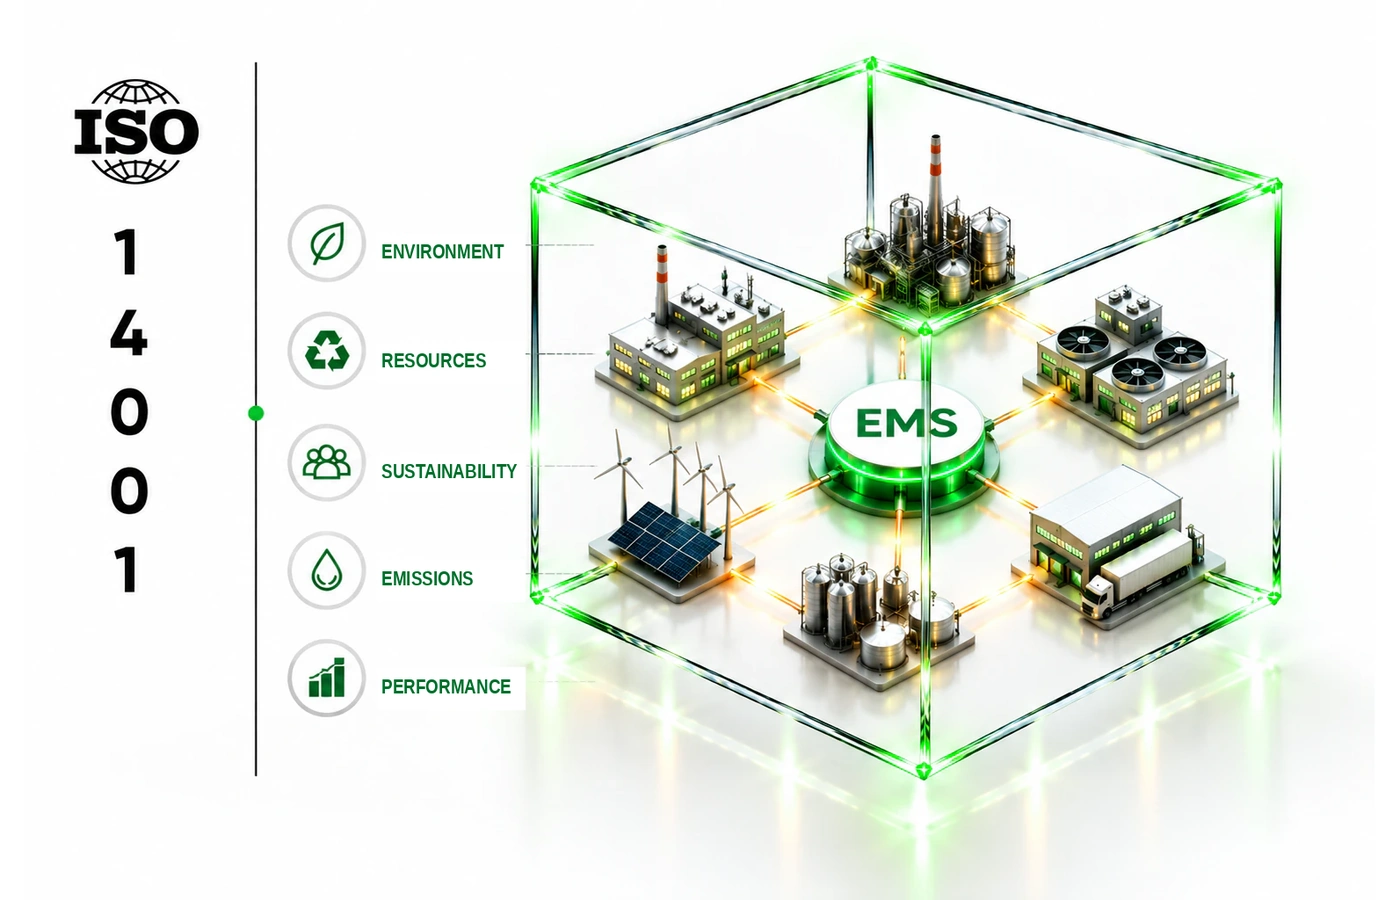
Environmental management for aspects, impacts, compliance obligations and environmental performance.
Learn more →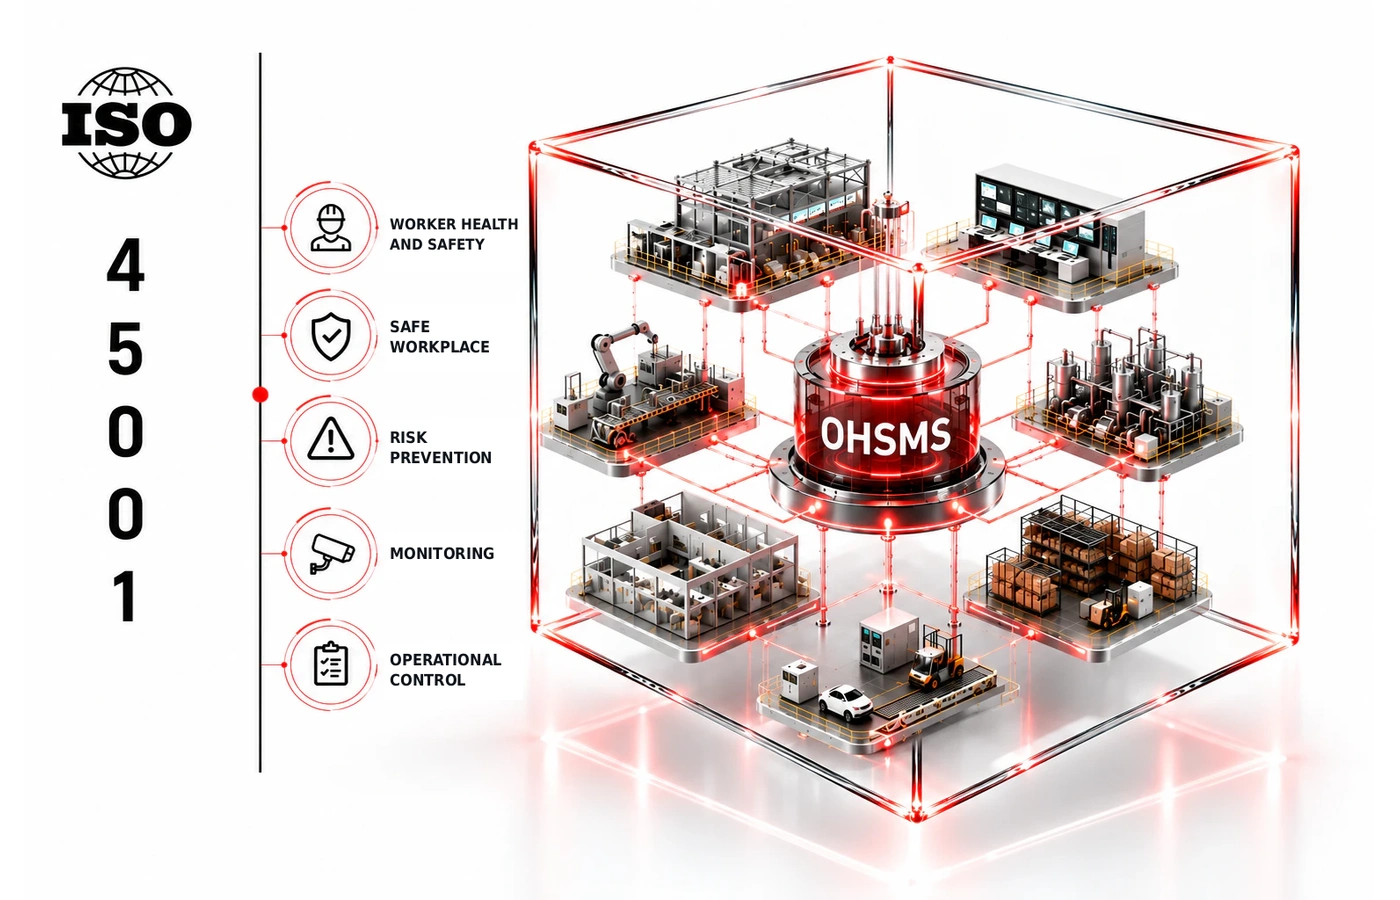
Occupational health and safety for OH&S risks, workers, contractors and prevention.
Learn more →
Checking the conformity and effectiveness of the system before certification, surveillance or recertification.
Learn more →
Evaluating suppliers, subcontractors and outsourced processes against the relevant requirements.
Learn more →
GAP analysis, implementation plan, documentation, training, operational support and audit preparation.
Learn more →
Reviewing evidence and corrective actions, and preparing the team for the certification body's audit.
Learn more →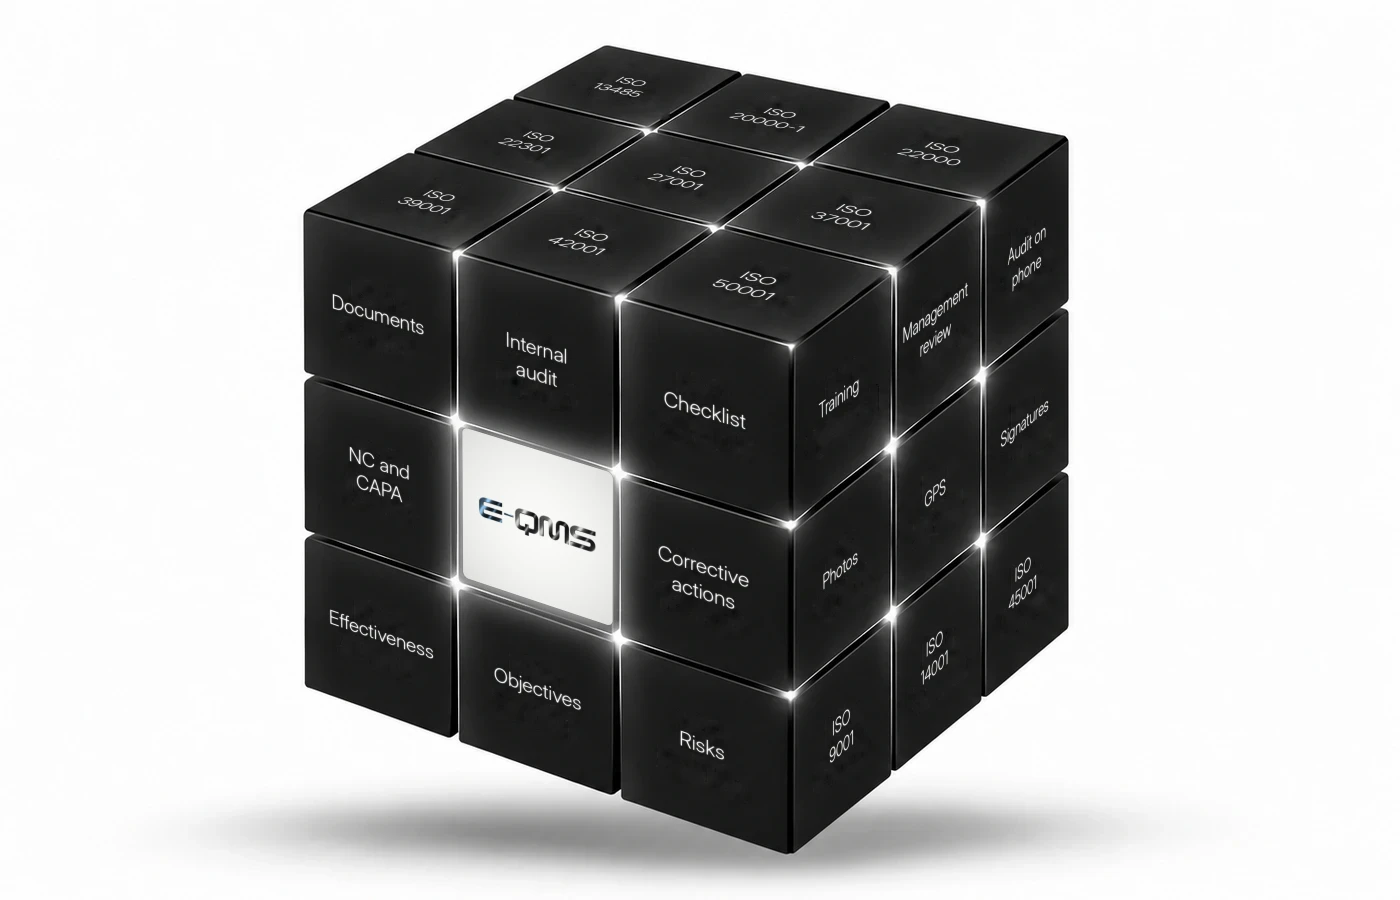
Documents, internal audit, nonconformities, corrective actions and management review, with alerts and reports generated automatically.
Learn more →
Developing internal competences for auditing management systems.
Learn more →
Advanced preparation for auditing management systems and coordinating audits.
Learn more →It is the international standard for anti-bribery management systems.
Direct and indirect bribery, in the public, private and non-profit sectors, depending on the context of the organization.
No. The standard helps with prevention, detection and response, but does not guarantee that the risk is completely eliminated.
Assessing the risks associated with relevant partners, transactions, projects, employees or third parties.
An independent certification body.
It depends on risks, size, processes, third parties, sensitive areas and the maturity of the compliance programme.
The anti-bribery policy, risk assessments, due diligence, controls, reports, investigations, the internal audit and the management review.
Yes, if the system is proportionate to the risks and complexity of the organization.
ISO 9001:2026 provides a process management structure, and ISO 37001:2025 adds anti-bribery controls.
The system is maintained through monitoring, internal audits, updating risks and surveillance audits.
Duration depends on the certification body, the size of the organization and the time needed to close any nonconformities. The stage 1 and stage 2 audits are scheduled together with the chosen body.
Choose a body with valid accreditation for the standard and your field of activity, where accreditation exists, and compare offers and audit conditions. The consultant does not certify and does not influence the body’s decision.
If your organization is aiming for ISO 37001:2025 certification, the services below turn the requirements of the standard into a working system: GAP analysis, useful documentation, training, internal audit and preparation for the certification body's audit.
We check whether the system is applied before certification, surveillance or recertification, and we prioritize corrective actions.
ISO internal audit →We build the system on real processes, risks, responsibilities, objective evidence and indicators relevant to bribery risks, due diligence and financial and non-financial controls.
ISO consulting →We prepare the team, the documents and the evidence for the certification audit, with a focus on effectiveness and conformity.
ISO certification preparation →Documents, internal audit, nonconformities, corrective actions and management review, with alerts and reports generated automatically.
Learn more →Services are available for organizations in Romania and the Republic of Moldova, including online work where the nature of the processes allows it.
Send us a few details about your organization, your field of activity and the goal of the project. We can guide you through the right steps for ISO 37001:2025 implementation, internal audit or certification preparation.
Phone: +40 722 773 446
Email: contact@qms.ro
Address: 12 Petru Rareș Street, Bucharest
Send an emailChoose whether to allow visitor statistics. You can change your choice at any time from the site footer.