Standard
ISO 27001:2022
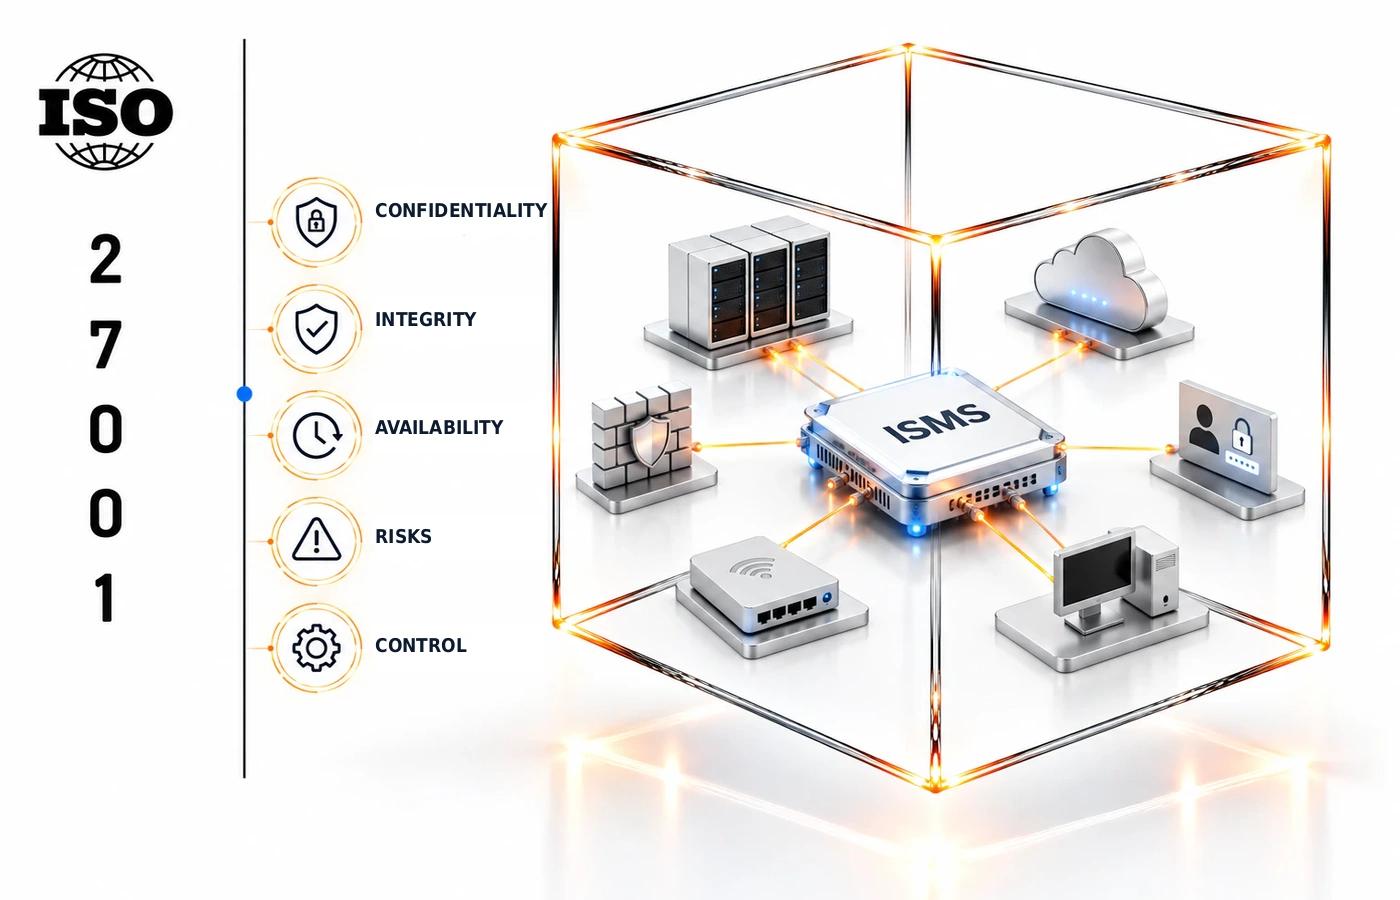
Structures the assessment and treatment of information risks, controls, access, incidents, suppliers and continuity.
Learn more →
Management systems for information security and IT services: risks, SLAs, cloud, incidents, changes, suppliers, internal audit and certification preparation.
IT&C organizations manage information, applications, infrastructure, cloud services and external dependencies. The management system must connect risks, contractual requirements and service objectives with responsibilities, controls and verifiable evidence.
QMS Consulting designs or optimizes ISO systems based on the organization's scope, the services provided, information assets, customers, suppliers and relevant incidents. Requirements are integrated into operations, support, development, changes and continuity, without parallel procedures.
ISO 27001:2022 structures information risk management, while ISO 20000-1:2018 structures IT service management. Common processes can be coordinated, while keeping the controls and evidence specific to each standard.
The choice depends on services, information, customers, suppliers, obligations and risks. ISO standards complement the applicable legal, contractual and regulatory requirements; they do not replace them.
Structures the assessment and treatment of information risks, controls, access, incidents, suppliers and continuity.
Learn more →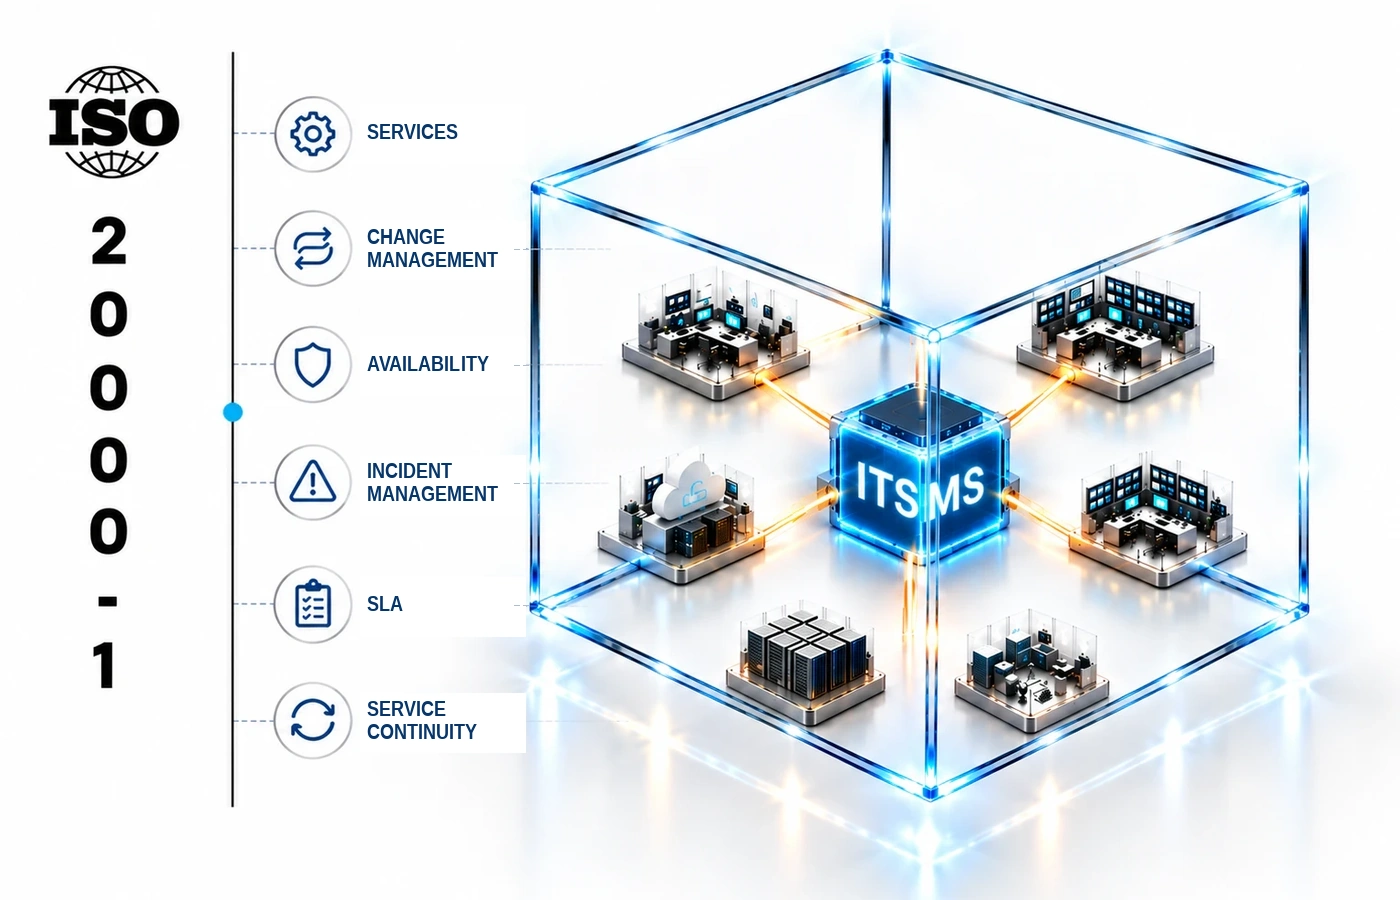
Supports the design, delivery, monitoring and improvement of IT services, including SLAs, incidents, changes and suppliers.
Learn more →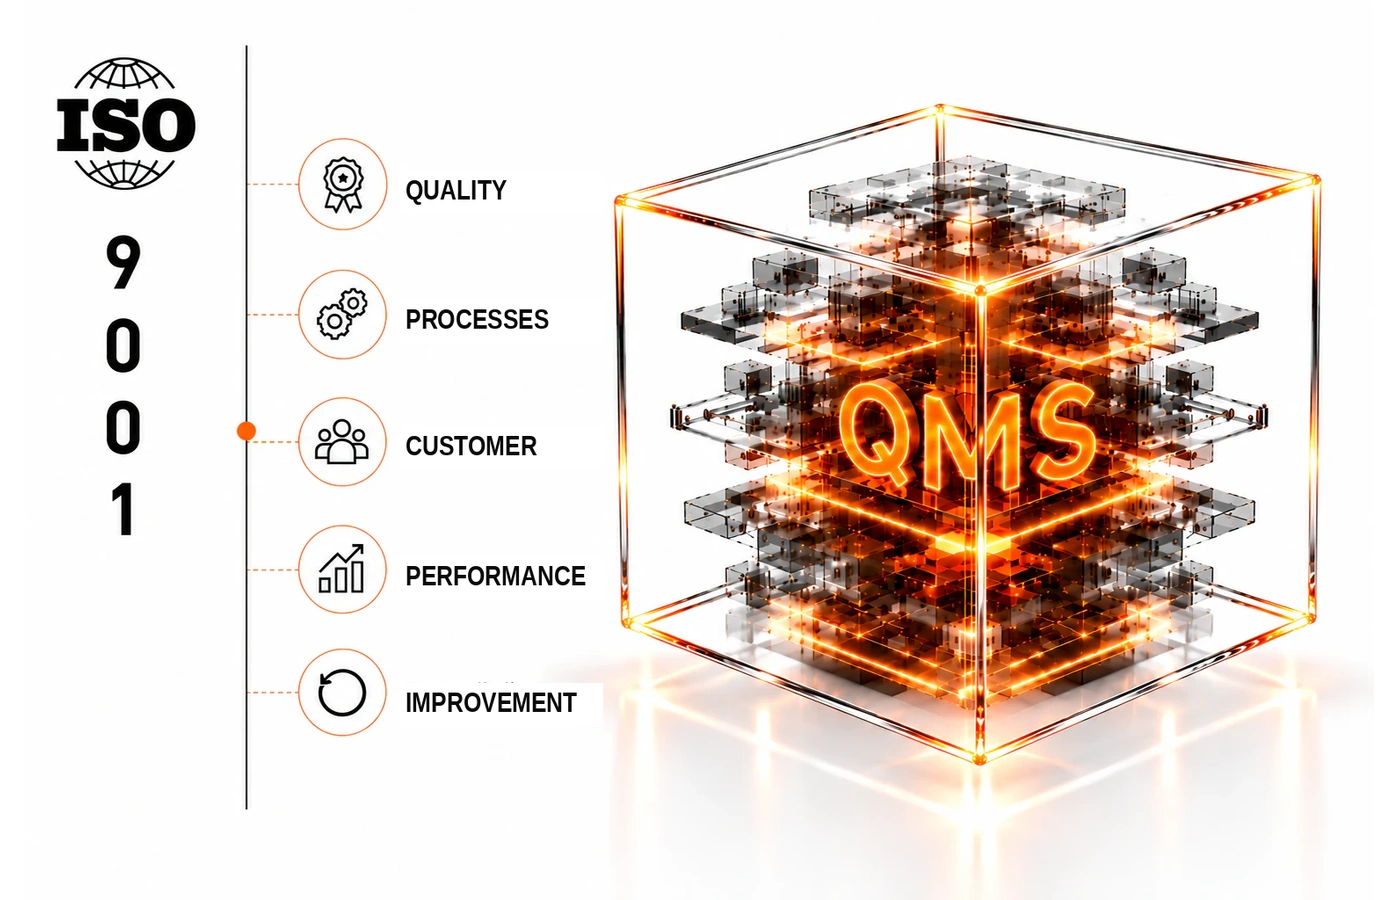
Clarifies processes, responsibilities, customer requirements, indicators, nonconformities and quality improvement.
Learn more →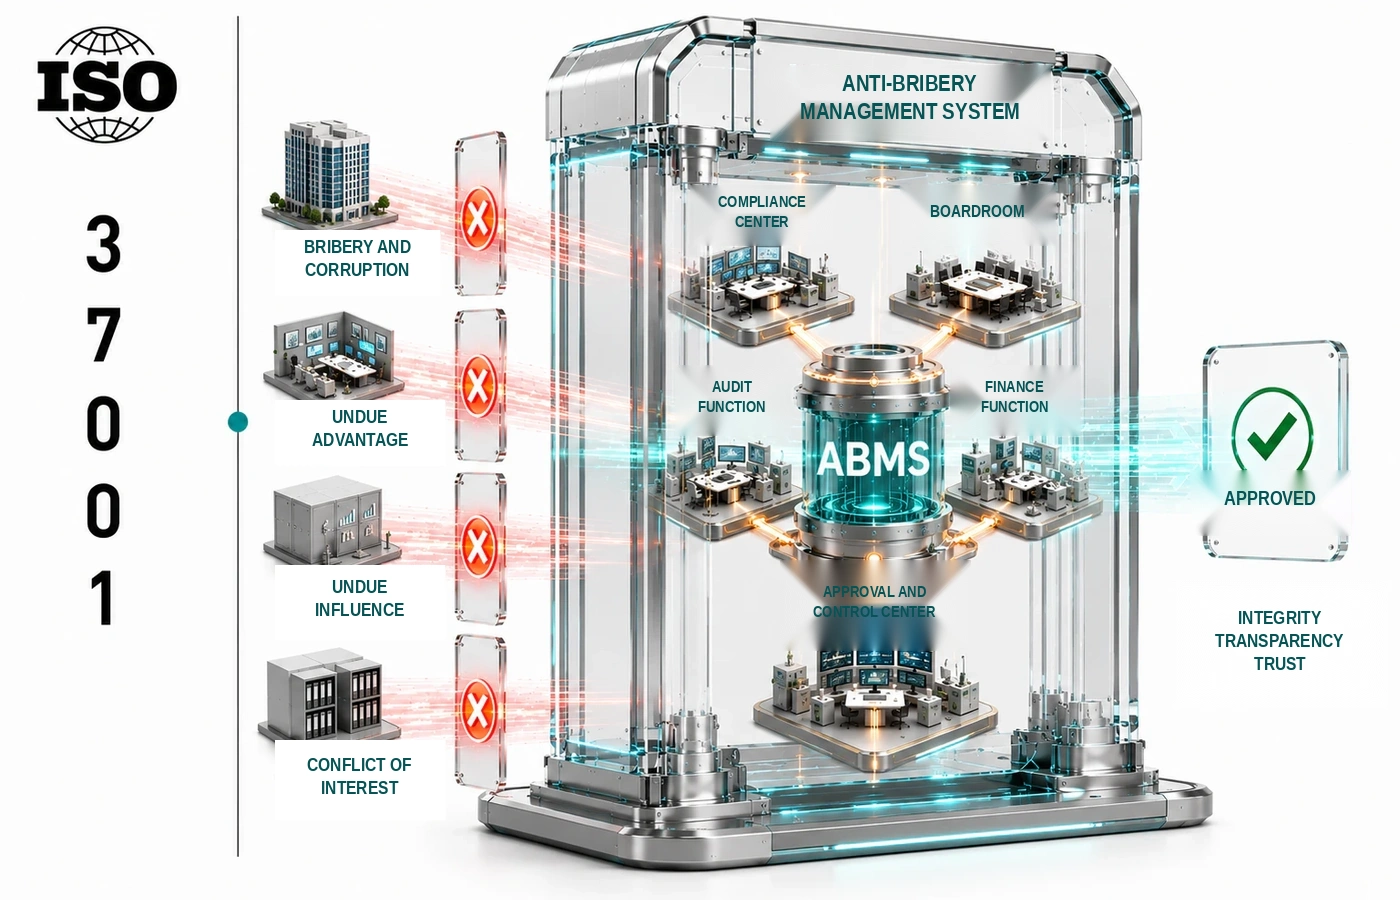
Provides a framework for bribery risk assessment, due diligence, controls and reporting mechanisms.
Learn more →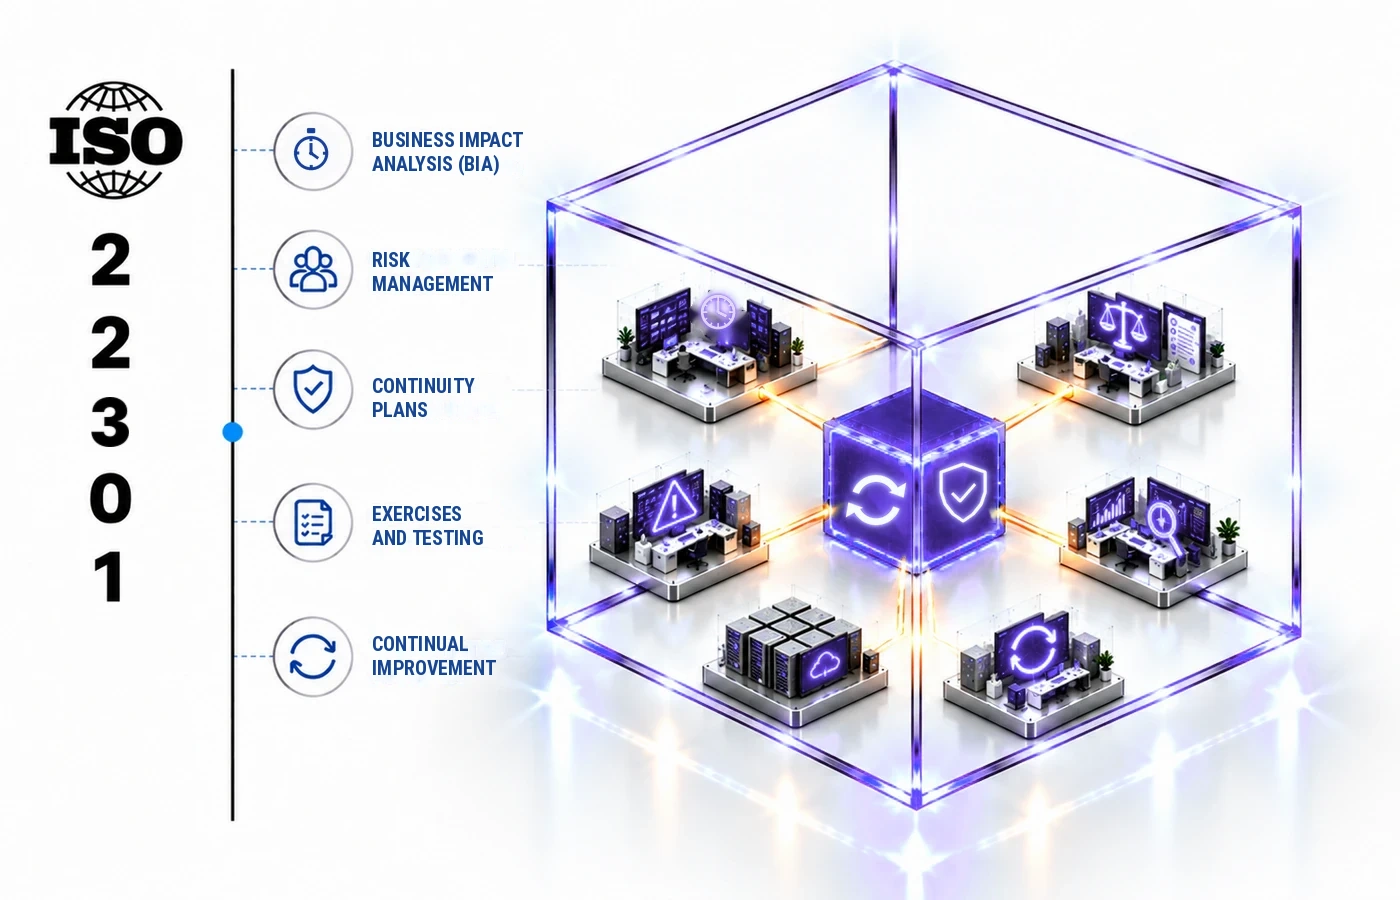
Supports the continuity of IT and cloud services through impact analysis, recovery plans and tested exercises.
Learn more →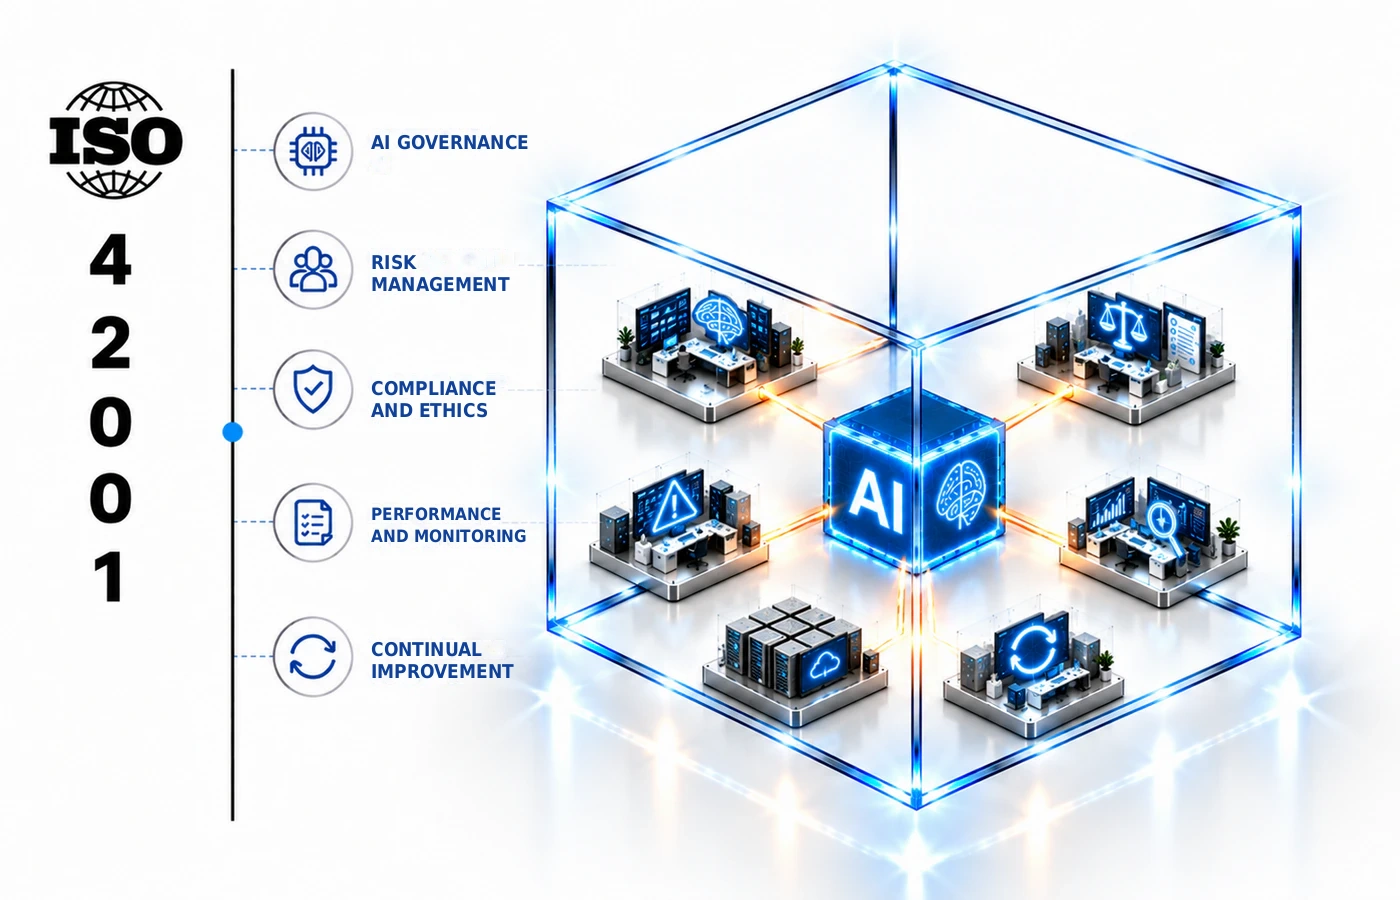
Provides a framework for the governance and control of AI systems developed or used in IT products and services.
Learn more →
Assessing conformity and effectiveness through interviews, sampling, documents and objective evidence.
Learn more →
Evaluating IT and cloud suppliers and other critical third parties by capability, control, continuity and performance.
Learn more →
GAP analysis, defining the scope, process design, proportionate documentation and implementation support.
Learn more →
Reviewing the system, checking evidence, addressing findings and preparing the team for the independent audit.
Learn more →
Documents, internal audit, nonconformities, corrective actions and management review, with alerts and reports generated automatically.
Learn more →
Practical training in planning, conducting, reporting and following up internal audits.
Learn more →
Advanced preparation for coordinating programmes, teams and complex or integrated audits.
Learn more →Controls must be assessed in relation to the real services, assets, users, suppliers, changes and disruption scenarios.
We link requirements to the services, processes, assets, responsibilities, indicators, suppliers and records available. Recommendations are prioritized by impact and integrated into existing mechanisms.
The value of the system appears when risks are addressed consistently, services are measured and incidents and changes are managed in a controlled way.
Risks are identified, assessed, treated and monitored through repeatable criteria and responsibilities.
SLAs, incidents, changes, capacity and availability are managed through clear processes and indicators.
Roles, classification, escalation, communication and post-incident review are defined and verified.
Evaluation and monitoring are adapted to criticality, access to information and the impact on services.
Scenarios, plans, backups and recovery capabilities are checked periodically.
Processes, decisions and records can be presented consistently in internal and external assessments.
The scope of the assessment is set according to the services included, assets, suppliers, sites, standards and level of risk.
The methodology, criteria, risk owners, treatment plans and acceptance of residual risk.
Controlling the life cycle of accounts and privileges, from request to review and revocation.
Detection, classification, escalation, response, communication and analysis of lessons learned.
Assessing, approving, testing, implementing and reviewing changes that affect services.
Evaluating, contracting and monitoring third parties, including obligations, performance, incidents and continuity.
Linking recovery objectives with critical services, tests, results and the improvements needed.
ISO 27001:2022 covers information security management, while ISO 20000-1:2018 covers IT service management.
No. It is relevant for any organization that must manage information risks systematically.
No. The standard supports systematic risk management, prevention, detection, response and improvement.
No. QMS Consulting provides consulting, audit, training and preparation. Certification is carried out by an independent body.
Yes. Common processes can be coordinated, while keeping the requirements and evidence specific to each standard.
The duration depends on the scope, services, infrastructure, suppliers, process maturity and available resources.
Documentation may include policies, risk assessments, procedures, registers, objectives, plans, audits and actions.
Yes. ISO 9001:2026 or other standards can be integrated when the processes, obligations and objectives justify it.
The configuration starts from services, information, processes, suppliers, obligations and risks, not from a generic model.
Common requirements are integrated to avoid duplicate procedures and records, while specific controls are kept where the standard, the service or the risk justifies them.
Send us your services, infrastructure, critical suppliers, target standards and the deadline you are aiming for. This information allows us to configure a realistic plan.
Phone: +40 722 773 446
Email: contact@qms.ro
Address: 12 Petru Rareș Street, Bucharest
Send the requestChoose whether to allow visitor statistics. You can change your choice at any time from the site footer.