Standard
ISO 9001:2026
Quality management for processes, responsibilities, indicators, customers and continual improvement.
Learn more →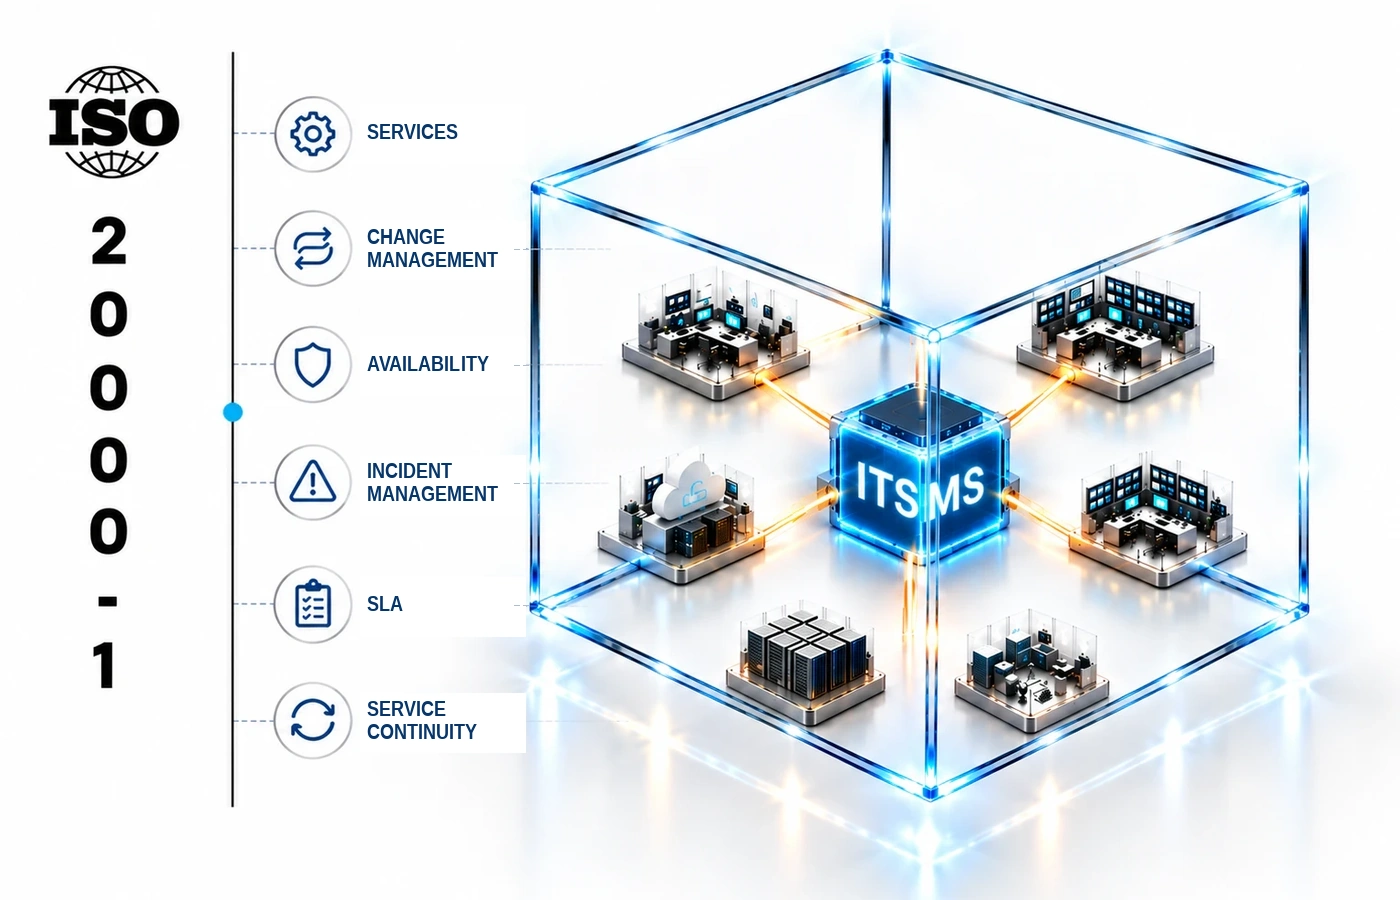
ISO/IEC 20000-1 implementation, IT service management system, SLAs, incidents, changes, availability, suppliers, internal audit and certification preparation.
ISO/IEC 20000-1:2018 is the international standard for the IT service management system. It sets requirements for planning, designing, transitioning, delivering and improving services, so that the organization provides value and meets service requirements.
Official title of the standard: ISO/IEC 20000-1:2018 — Information technology — Service management — Part 1: Service management system requirements.
QMS Consulting provides ISO/IEC 20000-1:2018 consulting for organizations that want a clear, applicable and auditable system. The aim is not just to obtain the certificate, but to build a system that supports process control, compliance and continual improvement.
ISO/IEC 20000-1:2018 is the reference edition for IT service management systems, and amendment ISO/IEC 20000-1:2018/Amd 1:2024 introduces changes related to climate action. The system must be built flexibly so that it stays aligned with current and future requirements.
ISO/IEC 20000-1:2018 requires IT services to be planned, delivered and improved within a controlled system, with clear responsibilities towards customers, suppliers and internal teams. The requirements apply in proportion to the service portfolio and the complexity of operations.
The service catalogue and SLAs are the starting point. Incident, problem and change processes only make sense if they support the promised service levels and can be demonstrated with data from the ITSM tools in use.
ISO/IEC 20000-1:2018 implementation starts from the services actually delivered and the existing ITSM tools. Each stage produces verifiable results: defined processes, service reports and audit evidence.
We compare existing ITSM practices with the requirements of the standard and identify missing or insufficiently documented processes.
We set the services included, internal and external customers, sites, suppliers and the interfaces with other management systems.
We define the workflows for incidents, requests, problems and changes, with roles, priorities, escalations and the link to SLAs.
We set objectives for availability, response times and customer satisfaction, together with periodic service reports.
We define the requirements for suppliers that deliver service components and how we monitor their performance.
We finalize the documentation, train the teams, carry out the internal audit of ITSM processes and prepare the management review based on service data.
We check the evidence, close the findings and prepare the team for the interviews and sampling of the certification audit.
ISO 20000-1 certification is obtained through an audit carried out by an independent certification body chosen by the organization. Consulting does not replace the audit: it prepares the system and the team for it.
The organization selects a certification body with valid accreditation for this standard, where accreditation exists, and agrees the audit dates with it.
The body reviews the documentation, the scope of the system and the organization’s readiness for stage 2. Points to fix before continuing may be raised.
The body verifies on site that the system is implemented and effective, through interviews, observation and evidence. Nonconformities found are closed through corrective actions.
After nonconformities are closed, the body takes the certification decision and issues the certificate. The system is then checked through surveillance and recertification audits, according to the body’s rules.
At every stage, a consultant dedicated to the project and consultants experienced in certification audits prepare the evidence, the team and the responses to nonconformities. The certificate is issued only by the certification body. See ISO certification preparation.
Requests, incidents and changes follow clear workflows, and delivery no longer depends on a few key people.
Service levels have indicators, owners and periodic reports that customers can check.
Prioritization, escalation and analysis of recurring problems reduce resolution times and the recurrence of incidents.
Certification demonstrates the maturity of ITSM processes to large customers and in tenders for IT services.
Components delivered by third parties have requirements, contracts and monitoring aligned with the SLAs committed to the customer.
Service reports show where delays and bottlenecks occur and support IT investment decisions.
ISO/IEC 20000-1:2018 is useful for IT, managed services and cloud providers, for IT departments in large organizations and for companies that deliver critical services based on SLAs.
ISO/IEC 20000-1:2018 is frequently combined with ISO/IEC 27001, because IT service management and information security work with the same assets, suppliers, incidents and changes.
Quality management for processes, responsibilities, indicators, customers and continual improvement.
Learn more →
Information security for information risks, the ISMS, controls, access and data.
Learn more →Business continuity for resilience, disruption scenarios and operational recovery.
Learn more →Privacy information management and extended controls for data protection.
Learn more →Business continuity for critical IT services: impact analysis, recovery plans and exercises.
Learn more →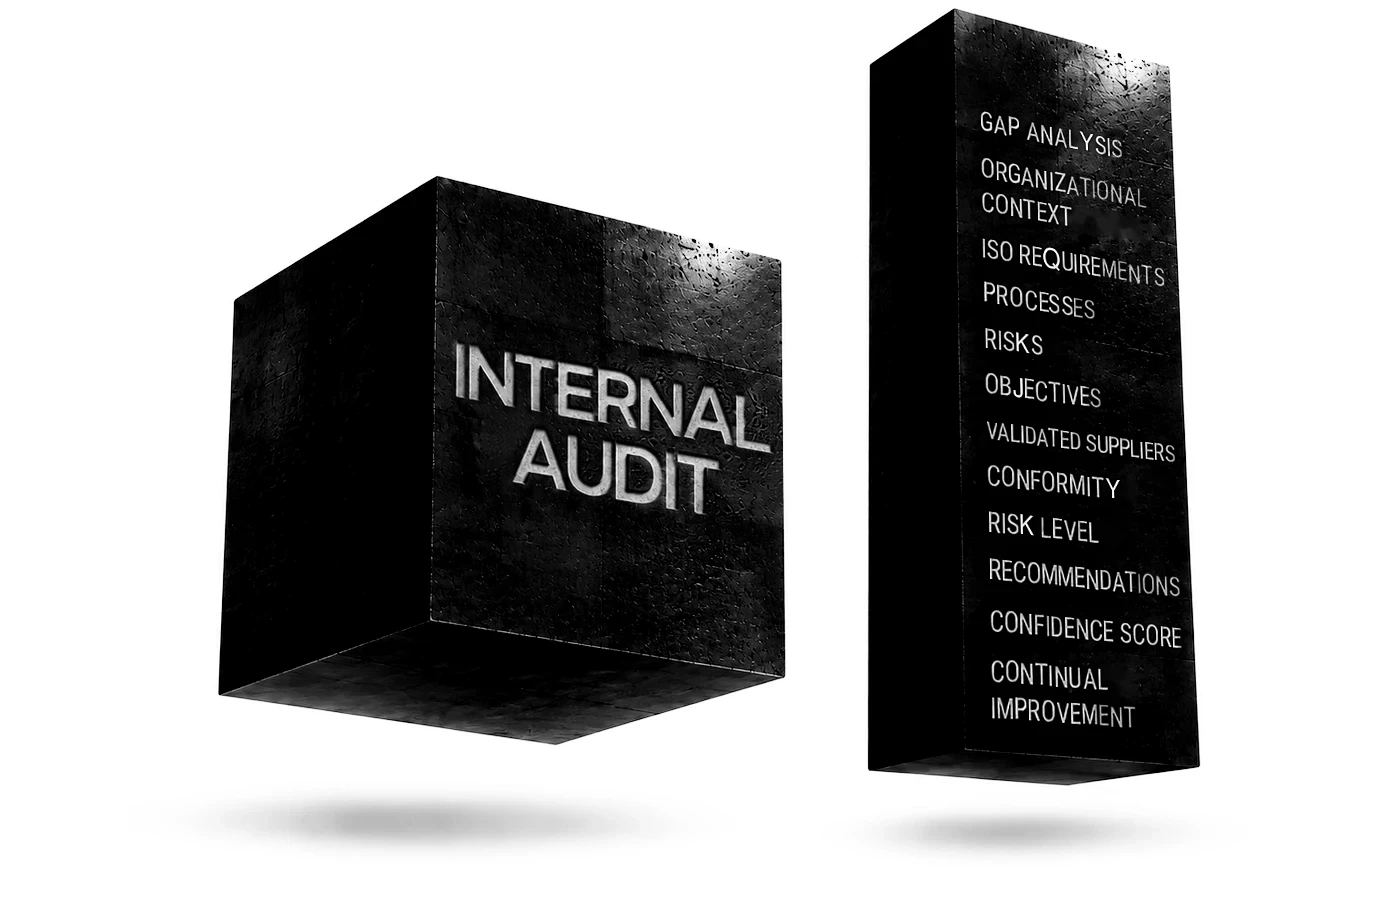
Checking the conformity and effectiveness of the system before certification, surveillance or recertification.
Learn more →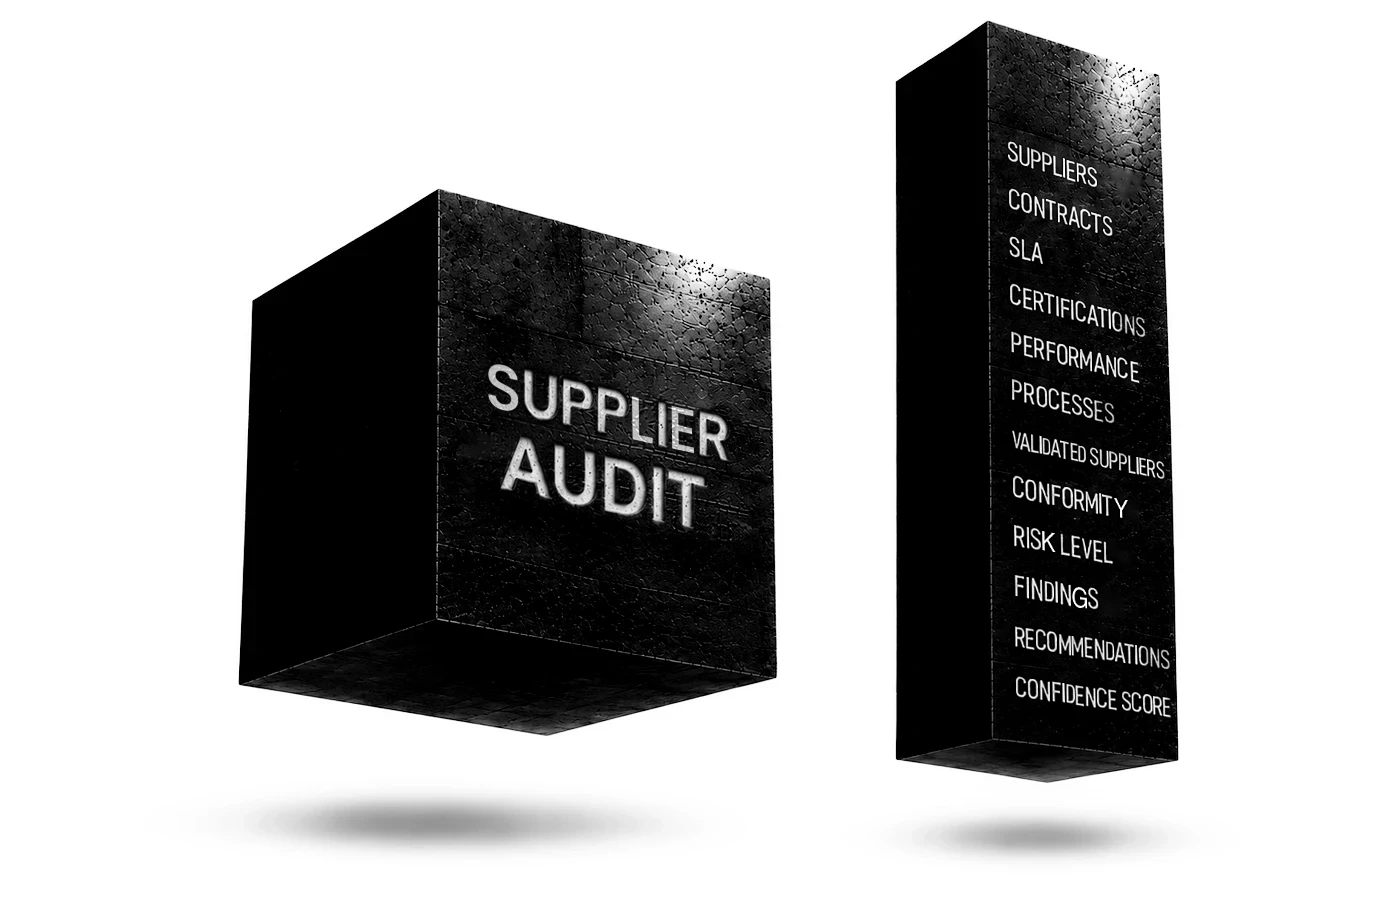
Evaluating suppliers, subcontractors and outsourced processes against the relevant requirements.
Learn more →
GAP analysis, implementation plan, documentation, training, operational support and audit preparation.
Learn more →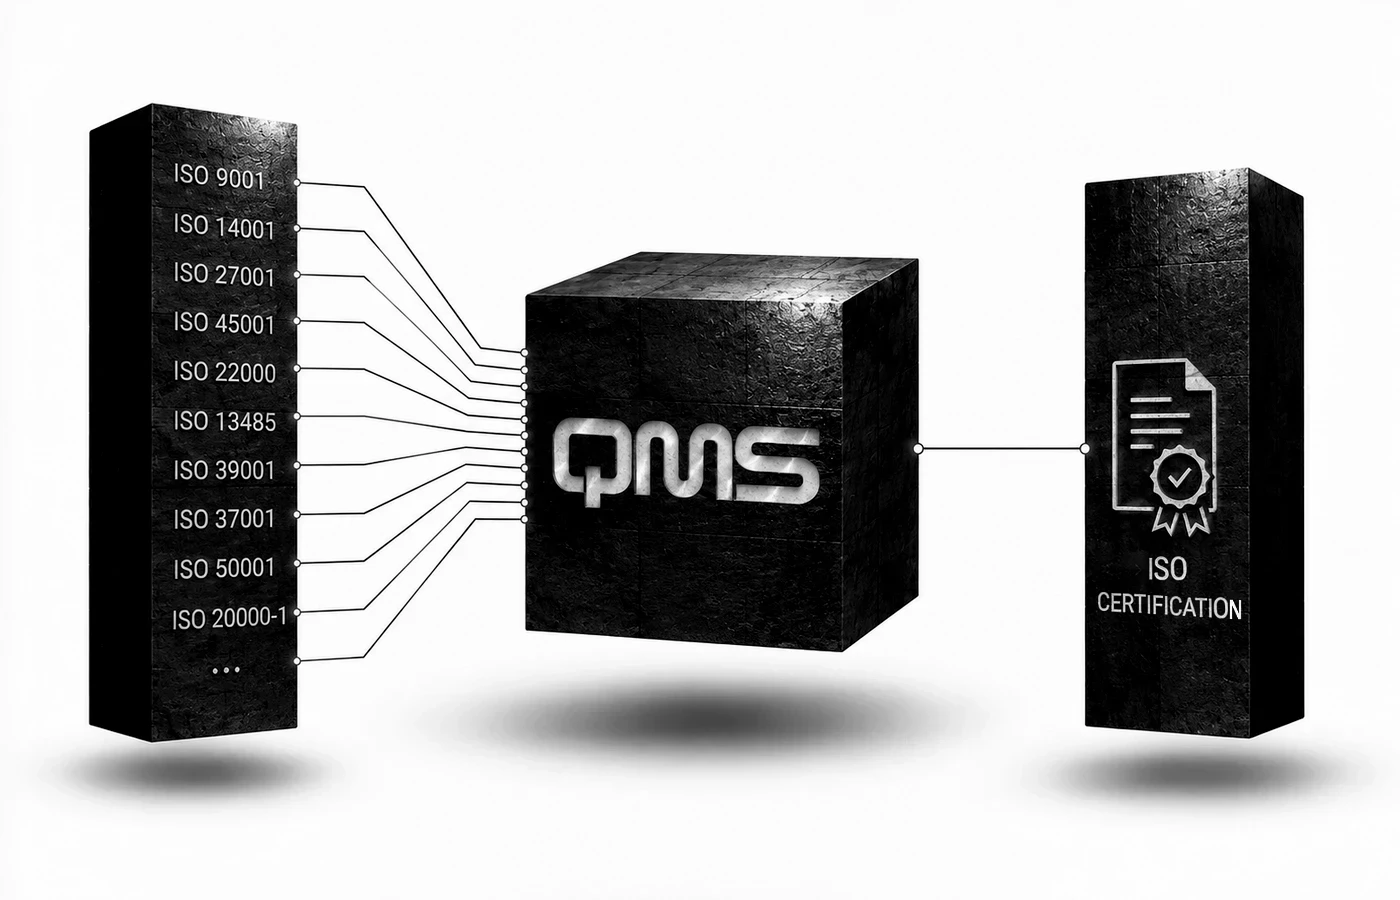
Reviewing evidence and corrective actions, and preparing the team for the certification body's audit.
Learn more →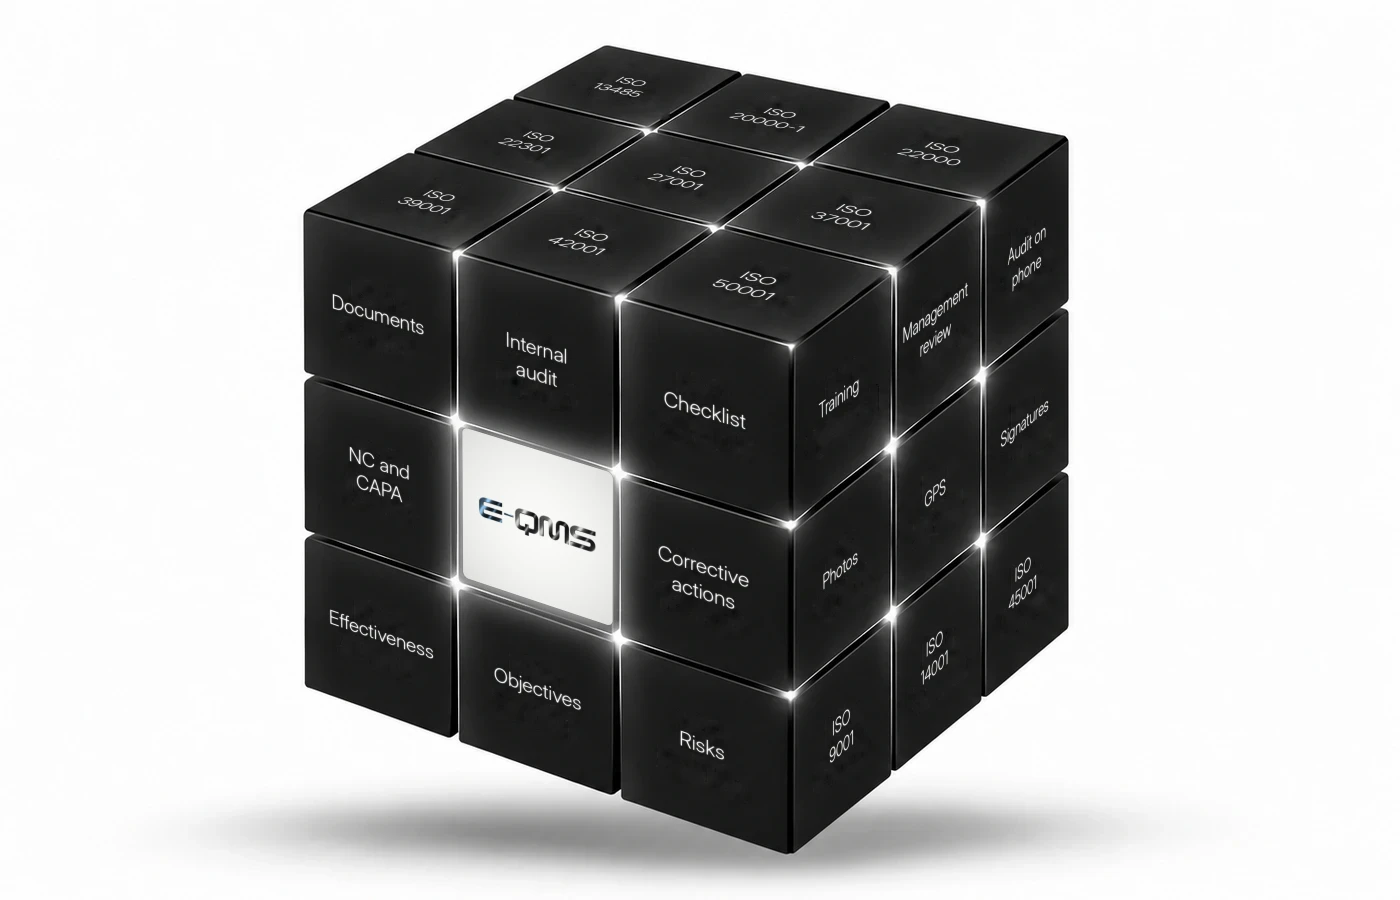
Documents, internal audit, nonconformities, corrective actions and management review, with alerts and reports generated automatically.
Learn more →
Developing internal competences for auditing management systems.
Learn more →
Advanced preparation for auditing management systems and coordinating audits.
Learn more →It is the standard for the IT service management system.
A Service Management System, i.e. the system through which the organization plans, delivers and improves its services.
IT providers, internal IT departments, SaaS companies, outsourcing and digital service providers.
An independent certification body.
GAP analysis, ITSM processes, SLAs, suppliers, incidents, changes, documentation, internal audit and preparation.
ISO 27001:2022 covers information security, while ISO 20000-1:2018 manages IT services; they are frequently integrated.
It depends on the services, customers, suppliers, existing ITSM processes and the maturity of the organization.
The SMS policy, service catalogue, SLAs, procedures, indicators, reports, internal audit and management review.
It is especially relevant for IT services, but it can be applied by any organization that manages IT services in a structured way.
The system is maintained through monitoring, internal audits, improvement and surveillance audits.
Duration depends on the certification body, the size of the organization and the time needed to close any nonconformities. The stage 1 and stage 2 audits are scheduled together with the chosen body.
Choose a body with valid accreditation for the standard and your field of activity, where accreditation exists, and compare offers and audit conditions. The consultant does not certify and does not influence the body’s decision.
If your organization is aiming for ISO/IEC 20000-1 certification, the services below turn the requirements of the standard into a working system: GAP analysis, useful documentation, training, internal audit and preparation for the certification body's audit.
We check whether the system is applied before certification, surveillance or recertification, and we prioritize corrective actions.
ISO internal audit →We build the system on real processes, risks, responsibilities, objective evidence and indicators relevant to SLAs, incidents, changes, continuity and service delivery.
ISO consulting →We prepare the team, the documents and the evidence for the certification audit, with a focus on effectiveness and conformity.
ISO certification preparation →Documents, internal audit, nonconformities, corrective actions and management review, with alerts and reports generated automatically.
Learn more →Services are available for organizations in Romania and the Republic of Moldova, including online work where the nature of the processes allows it.
Send us a few details about your organization, your field of activity and the goal of the project. We can guide you through the right steps for ISO 20000-1:2018 implementation, internal audit or certification preparation.
Phone: +40 722 773 446
Email: contact@qms.ro
Address: 12 Petru Rareș Street, Bucharest
Send an emailChoose whether to allow visitor statistics. You can change your choice at any time from the site footer.